Governed Data Exchange, Inside the ServiceNow AI Platform
ServiceNow runs your IT service, operations, assets, security, HR, and customer work, and every one of those workflows moves sensitive files. Incidents collect logs and screenshots, asset audits pass around contracts and inventories, and HR cases carry identity and medical documents, and those files travel as attachments and email, outside company data policy. Opening the platform to vendors, auditors, and customers only widens that exposure. Verizon’s 2026 Data Breach Investigations Report attributes 48% of breaches to third parties.
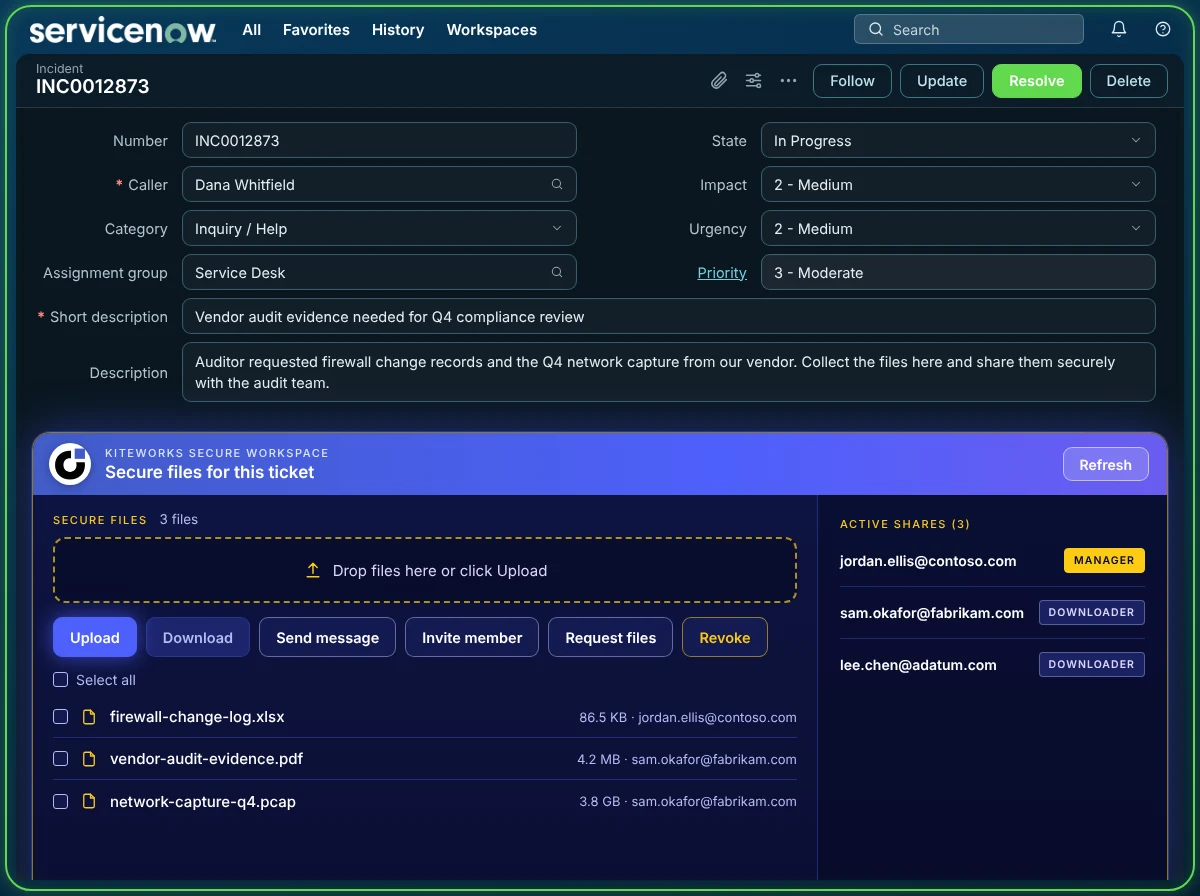
Kiteworks for the ServiceNow AI Platform adds a governed Kiteworks folder to the record. Teams send secure email, keep files in governed folders, and request files from vendors, auditors, and customers without leaving the record. The Kiteworks Data Policy Engine evaluates each file, transfers run up to 16 TB, and the evidence stays on the record, so each of the eight use cases below keeps the workflow you already run and gains the control it has been missing.
Work With Files Without Leaving the Ticket
From the record, people upload files, send secure email, and request files from vendors, auditors, and customers. A file request goes out as a secure link, so outside parties upload through it and need no ServiceNow AI Platform access.
Large files are not a problem, because transfers run up to 16 TB. Everyone works from the ticket they already have open, and the files stay in governed storage.
The Ticket Data Governance Test
Four questions separate a ticket with governed files from a ticket with files at risk.
Contain
Where does the file go, and who owns it?
Files live in a governed Kiteworks folder, not in ServiceNow AI Platform attachment storage, encrypted in transit and at rest. Choose on-premises, self-hosted, Kiteworks-hosted, FedRAMP, or IRAP, with single-tenant architecture, customer-owned keys, and geofencing.
Control
Does every file follow policy?
The Data Policy Engine evaluates the sensitivity of the data and the current attributes of the user, then blocks the transfer, limits to view only, requires approval, or tags the file. The scan verdict is checked before download.
Prove
Can you show an examiner what happened?
Governance Events record what people do through the app, on the record. The Kiteworks audit log records all file activity and streams to your SIEM.
Move
Does it keep people working?
Secure email, governed folders, and file requests, all from the record. Transfers run up to 16 TB, so there is no practical size limit. Outside parties need no ServiceNow AI Platform access.
Kiteworks-Governed Data Exchange on Every ServiceNow Record
Governed folder
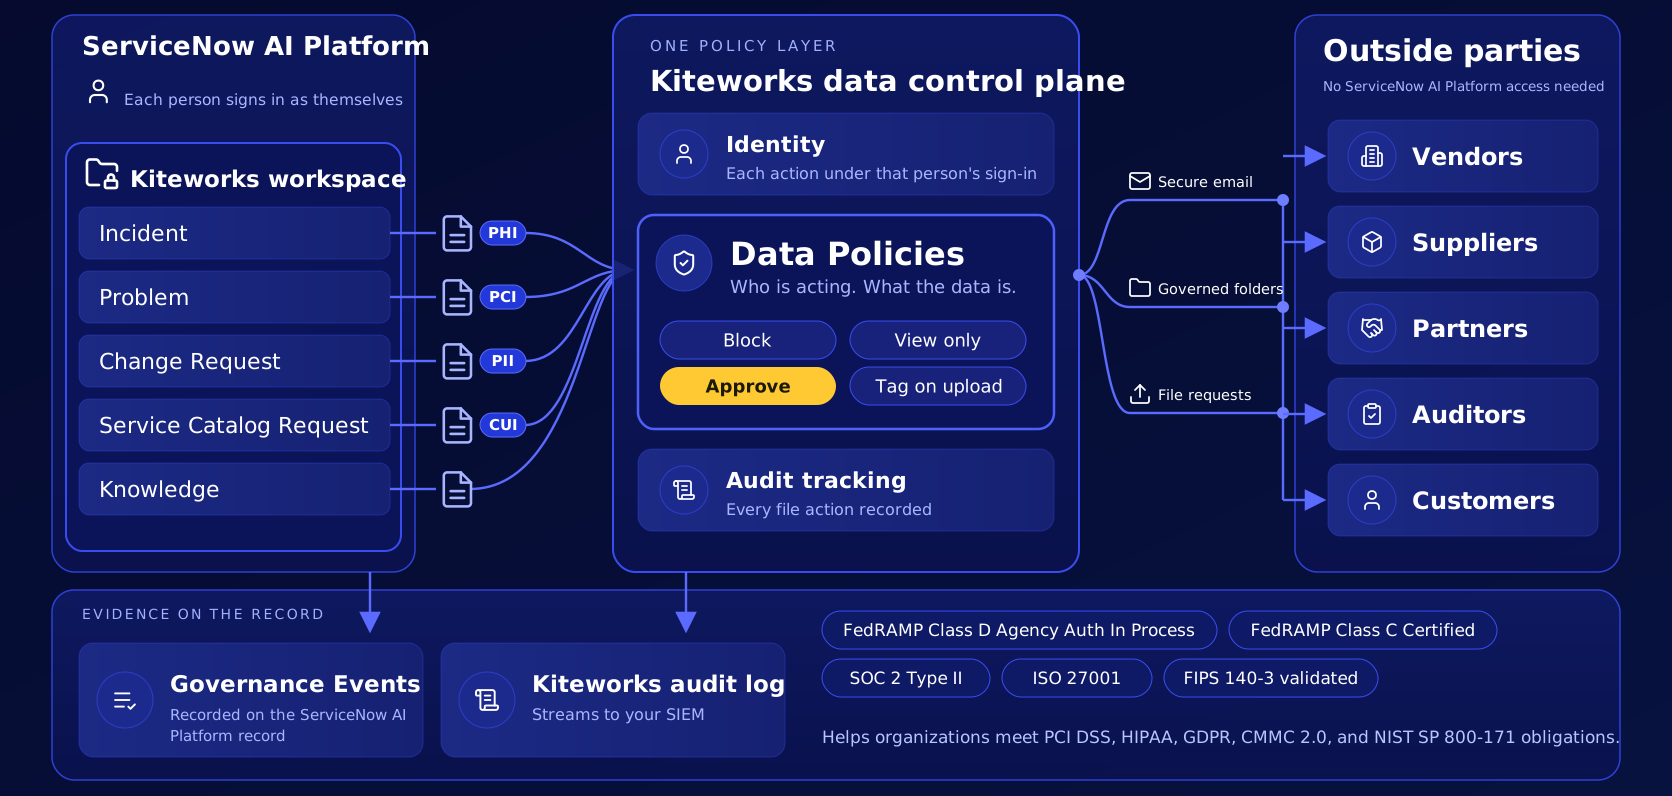
One Kiteworks folder tied to one record, created the first time someone opens the record’s Kiteworks panel. Files are protected and stored in Kiteworks, and nothing is written to ServiceNow AI Platform attachment storage.
Data Policy Engine
Evaluates each data access or movement request based on the data sensitivity, such as PHI, PCI, PII, or CUI, and the attributes and privileges of the actor, using role-based and attribute-based access control policies. As a result, it blocks the action, limits the user to view only, requires approval, allows the action, or tags the file to control later processing.
Every action audited
Governance Events record what people do through the app, including refused actions, on the ServiceNow AI Platform record. The Kiteworks audit log records all file activity and streams to your SIEM.
File request
Sent from the record to an outside party, who uploads through a secure link. Vendors, suppliers, partners, auditors, and customers need no ServiceNow AI Platform access.
Credentials
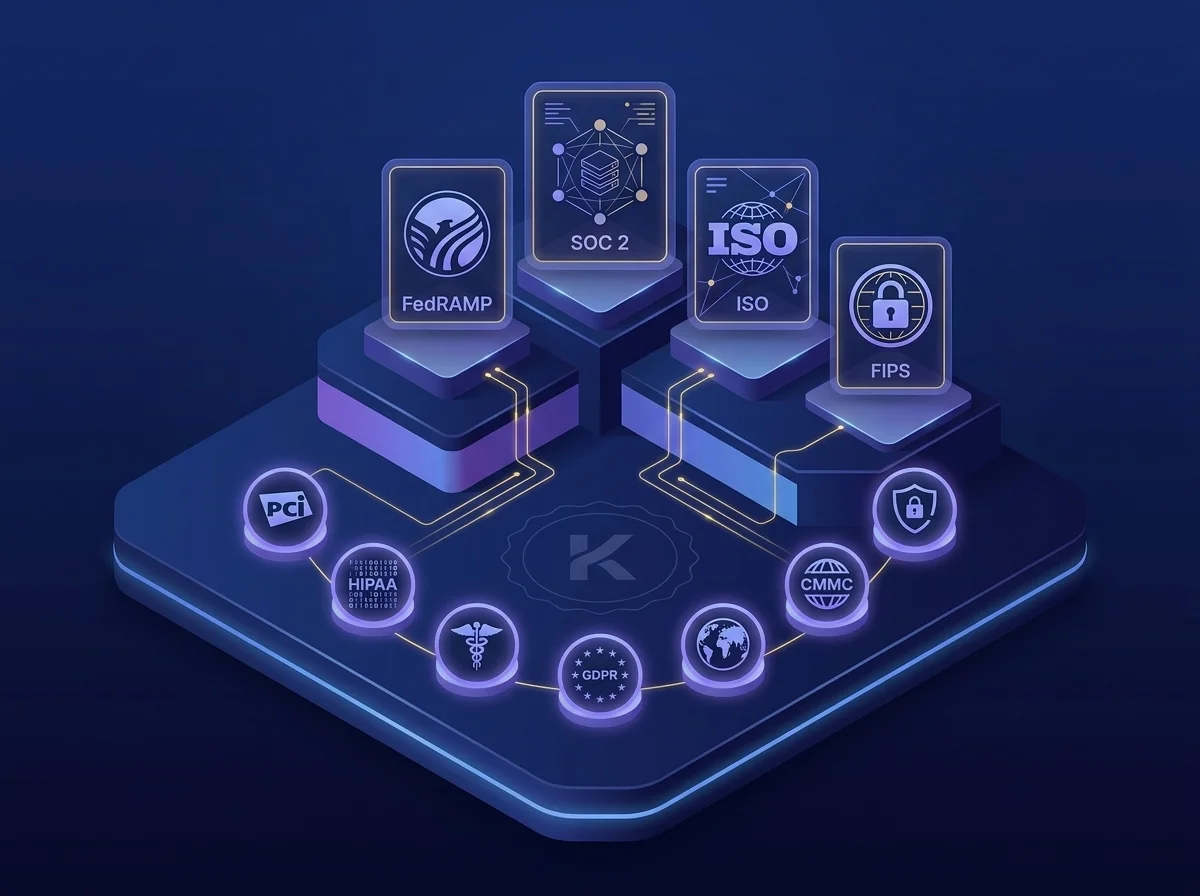
Kiteworks maintains a broad set of security and compliance certifications, including:
- FedRAMP Class D Agency Auth In Process and FedRAMP Class C Certified
- FIPS 140-3 Validation
- SOC 2 Type II
- ISO 27001, 27017, 27018
- BSI C5
Kiteworks helps organizations meet an even broader set of regulations, including:
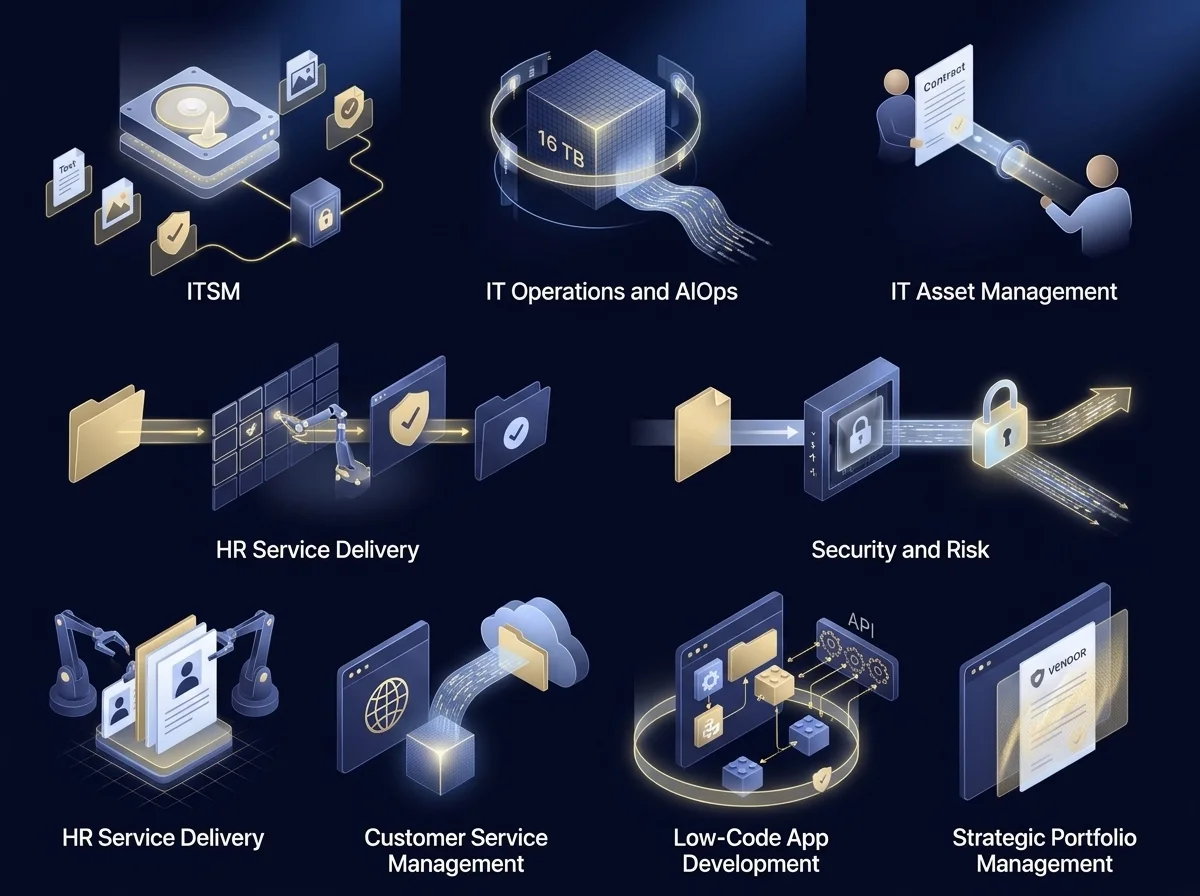
How Kiteworks Governs Data in Eight ServiceNow Workflows
Read on for descriptions of how Kiteworks improves governance and security of each of these use cases:
- IT Service Management: Logs, screenshots, and vendor evidence stay in governed folders.
- IT Operations and AIOps: Diagnostic and capture files up to 16 TB are scanned and auditable.
- IT Asset Management: Shared contracts and license files produce a record of who received what.
- Security and Risk: Inbound files are scanned, evidence is sent encrypted, and activity is fed to your SIEM.
- HR Service Delivery: ID and medical documents are handled by policy, not by habit.
- Customer Service Management: Customers upload from a browser, very large files included.
- Low-Code App Development: Apps built on Kiteworks REST APIs inherit governed file handling.
- Strategic Portfolio Management: Vendor documents are shared view-only and watermarked.
IT Service Management Administration
ServiceNow Platform Owner, Administrator, Developer, ITSM Process Owner
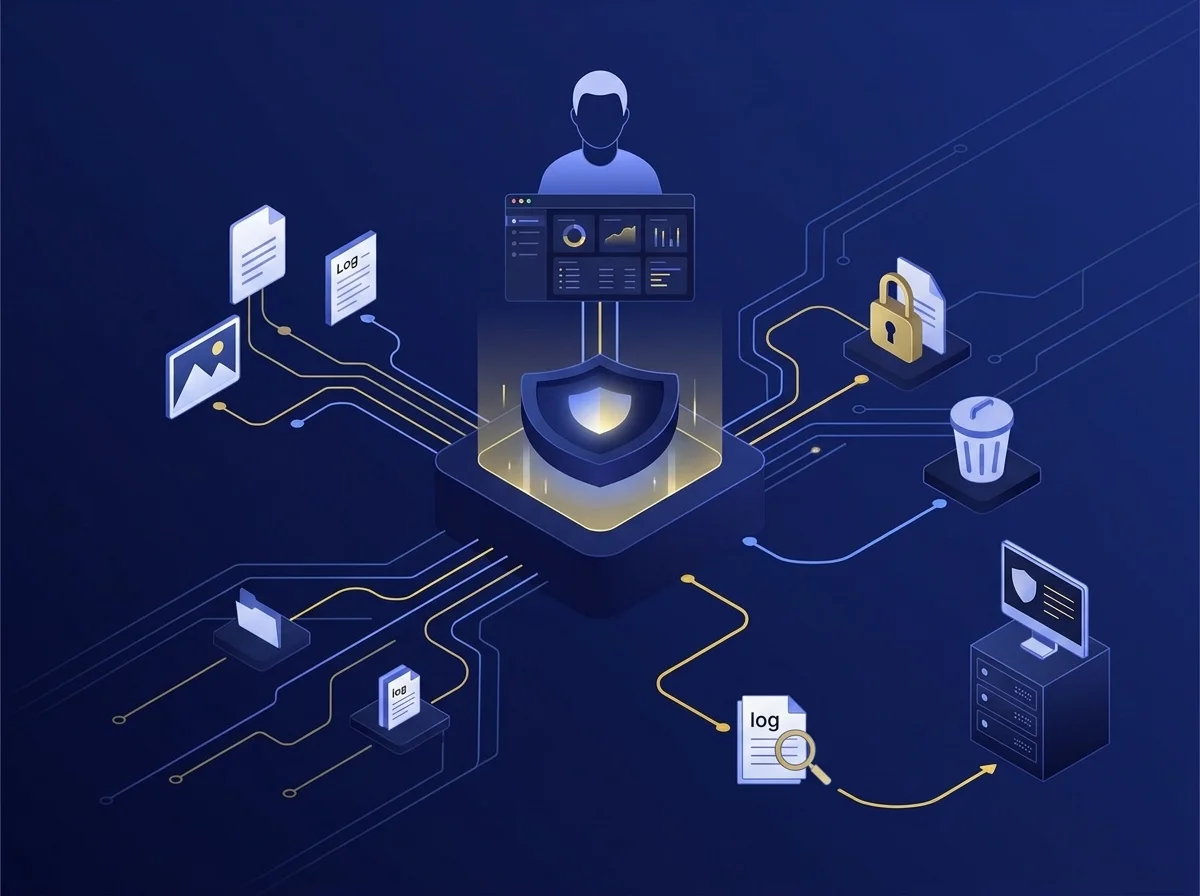
Every day, tickets arrive carrying screenshots, logs, and documents that hold personal or regulated data, and the platform owner is the person asked to prove who received what. Without a single policy and audit log, answering means assembling evidence by hand, and any gap becomes an audit finding the owner is accountable for.
With Kiteworks, the owner defines data policies for ticket attachments and email in one place. Sensitive files are blocked or encrypted, expiration and retention follow policy, and one audit log goes to the SIEM.
IT Service Management Users
Service Desk Analyst, Incident, Change, and Problem Manager, all employees
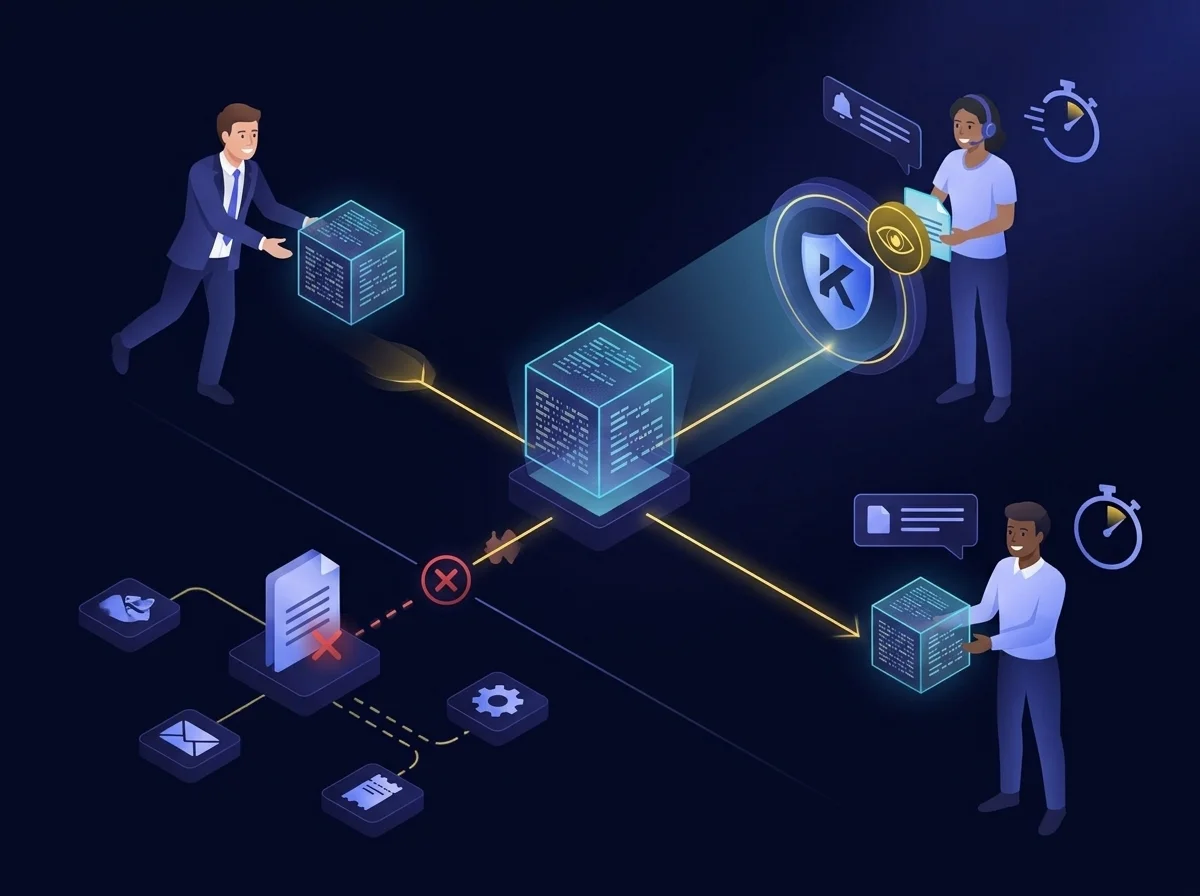
A service desk analyst needs a log file from an employee, but the file is too big to attach, so the ticket stalls while the two trade emails and hunt for a workaround. On the highest-volume workflow in the platform, that back-and-forth stretches resolution times. With Kiteworks, the analyst requests logs and screenshots through a secure link with no size limit, and the employee uploads straight from the ticket. The analyst can see whether recipients opened what was sent, so there is less chasing, safer exchange, and faster resolution.
IT Operations Management and AIOps Administration
CMDB Administrator, ITOM Platform Engineer, ServiceNow Architect
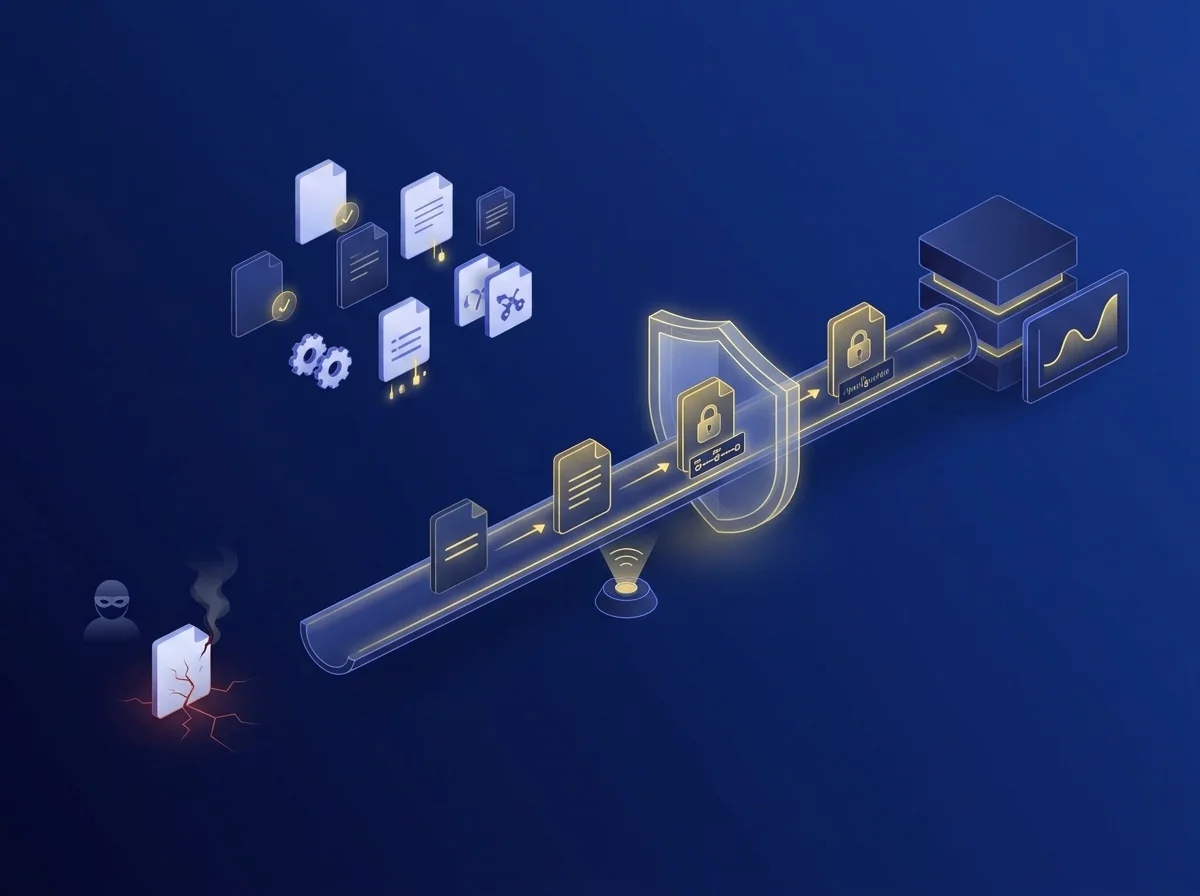
Configuration files and diagnostic bundles map the environment for an attacker. When one leaks through an unmanaged transfer, the exposure falls on the team that owns the CMDB, and paying for control up front is cheaper than explaining the leak afterward. With Kiteworks, diagnostic bundles and configuration files that leave the company move through a governed, scanned, and auditable channel. The CMDB administrator can show how each file left, under which policy, instead of reconstructing the trail after an incident has already put the environment at risk.
IT Operations Management and AIOps Users
NOC Analyst, Site Reliability Engineer, Infrastructure and Cloud Engineer
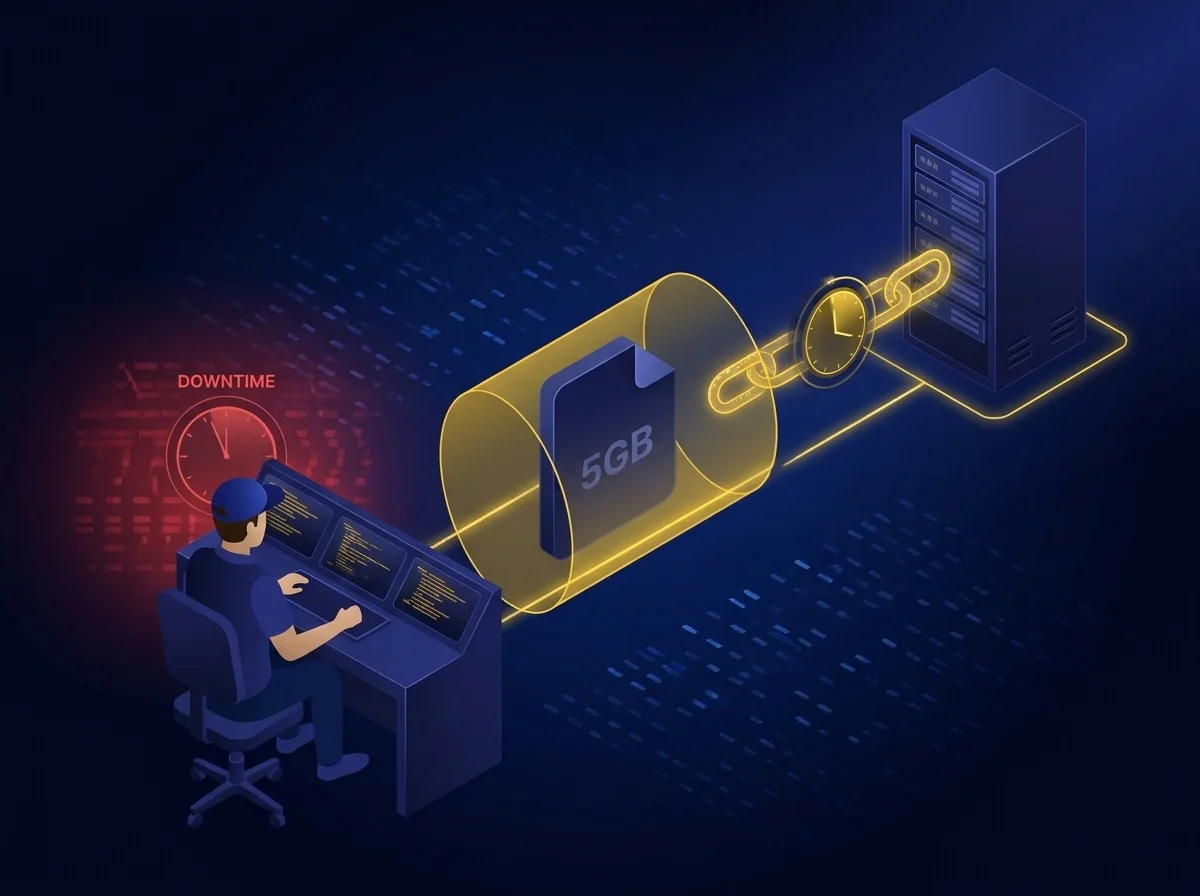
During an outage, a site reliability engineer has a 5 GB packet capture that the vendor needs immediately. Every minute spent finding a way to send it extends the downtime, and the usual workarounds are either slow or unsafe. With Kiteworks, the engineer exchanges large logs and captures with the vendor through a secure channel, using expiring links, so the file moves while the incident is still open. A reliable vendor channel directly shortens the time to restore service, and the link closes when the work is done.
IT Asset Management Administration
IT Asset Manager, Software Asset Manager, ITAM Administrator
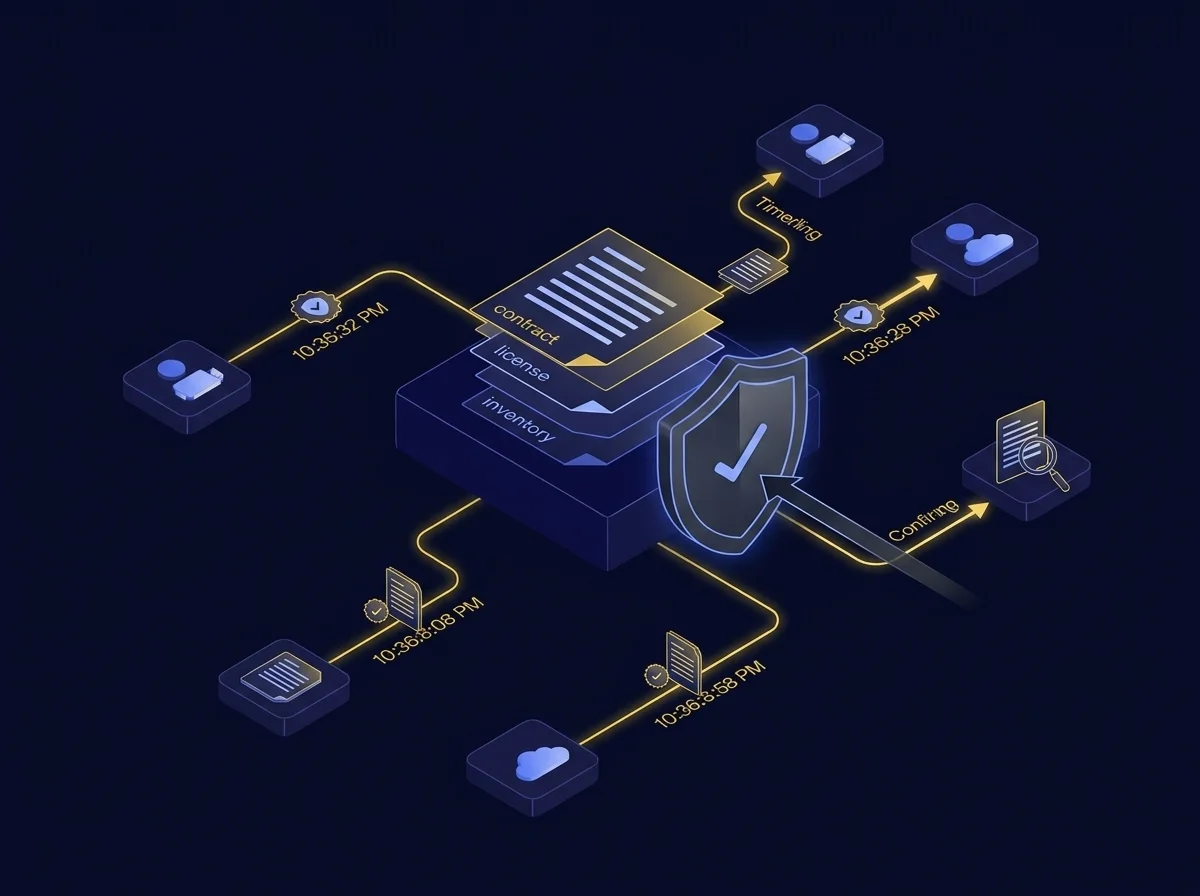
A software vendor opens a license audit, and the asset manager has to produce contracts, license files, and inventories. Audits can end in true-up payments, and reconstructing what was shared, with whom, and when takes hours nobody planned for. With Kiteworks, contracts, license files, and inventories shared with vendors and auditors are tracked from the first send. The asset team holds defensible evidence of exactly what was shared and when, which helps avoid paying more than is owed and cuts the time spent rebuilding the record.
IT Asset Management Users
Procurement Specialist, FinOps Analyst, Software Licensing Analyst
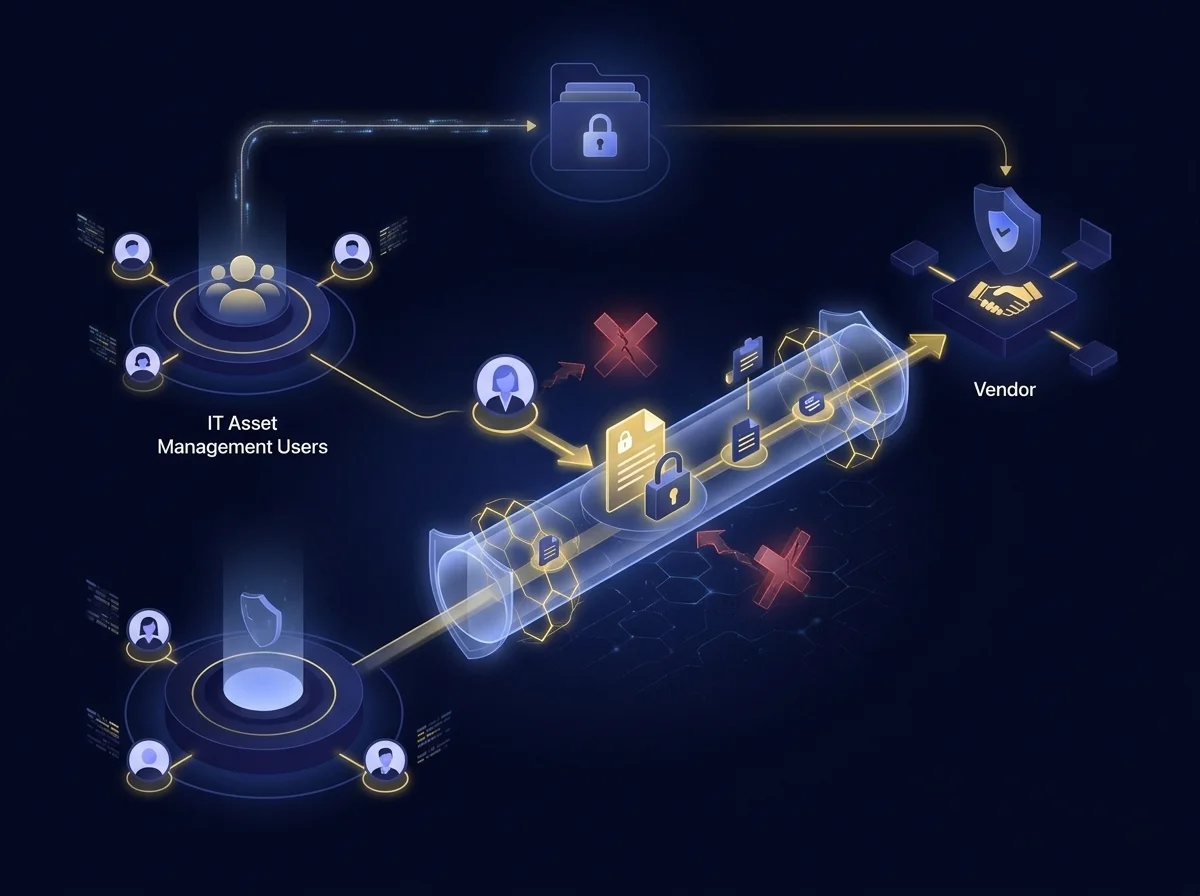
A procurement specialist negotiating a renewal needs to trade quotes and audit evidence with a vendor, and the quickest route is personal email, which nobody can audit later. Pricing and contract terms are commercially sensitive, so that shortcut puts negotiating position at risk and raises a compliance question on every deal. With Kiteworks, the specialist sends and receives quotes and audit evidence through a secure channel, without personal email. Sensitive terms stay protected, the deal keeps its pace, and nobody has to explain later where the files went.
Security and Risk Administration
Security Platform Owner, SecOps and GRC Administrator, GRC Program Manager
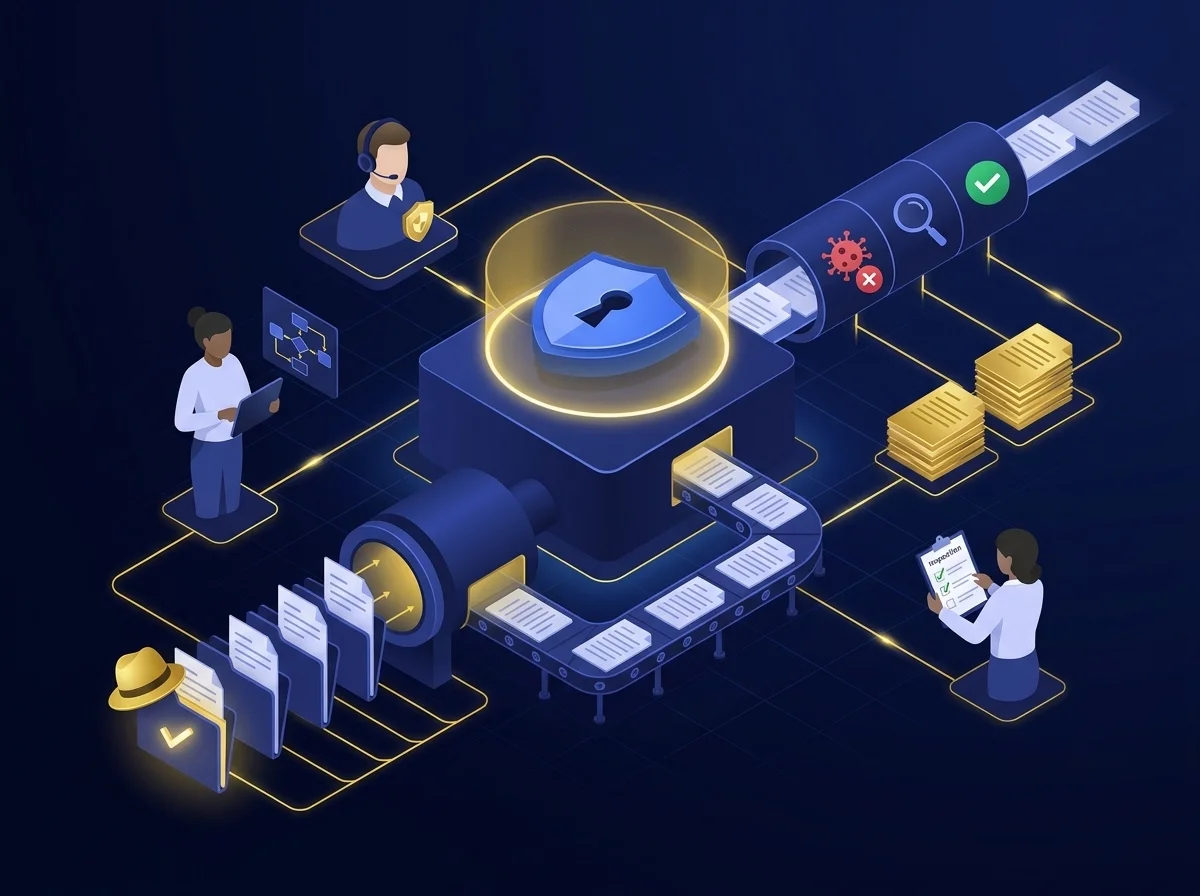
A security team is judged by the standard it enforces. Inbound files that skip scanning, and evidence transfers that nobody logged, weaken incident response and fail audits, and the fines under DORA, HIPAA, and GDPR, plus lost contracts, can far exceed the cost of the control. With Kiteworks, inbound files pass through antivirus checks, and optionally DLP and CDR, before anyone opens them. Activity feeds Splunk or ArcSight, and compliance reports are built in, so the security platform owner has the evidence ready when an examiner asks.
Security and Risk Users
SOC Analyst, Vulnerability Analyst, Compliance Officer, Internal Auditor, Risk Manager
A SOC analyst receives a suspected malware sample, and a compliance officer has to send control evidence to an auditor. Neither should have to choose between speed and safety, yet without a safe path they improvise, and mishandled evidence creates risk of its own. With Kiteworks, analysts collect samples and control evidence through a built-in safe path, and forensics go to auditors and regulators encrypted. The built-in route saves hours in every audit cycle and removes the risk of mishandling evidence along the way, for analysts and auditors alike.
HR Service Delivery Administration
HRSD Platform Owner, HRIS Analyst, HR Operations Manager
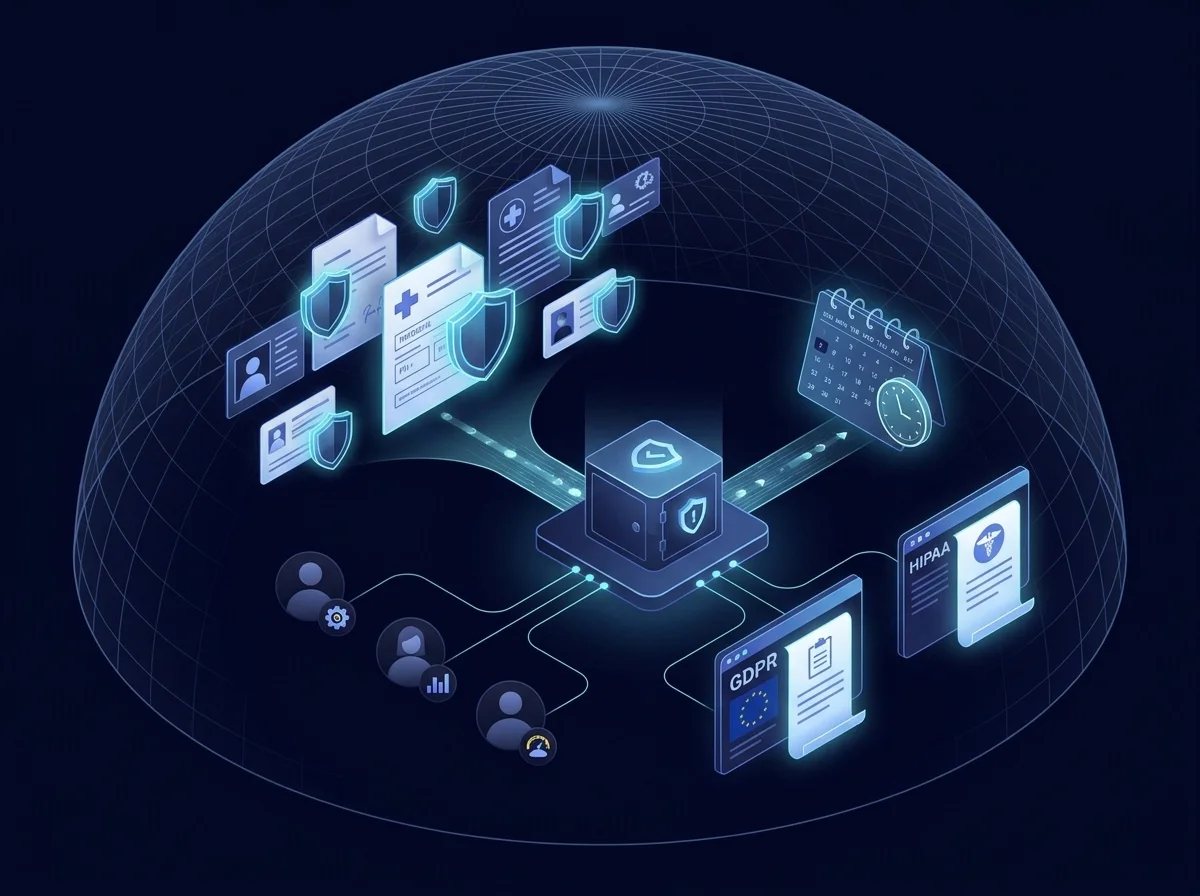
HR cases hold the most personal data in the company: identity documents, medical records, and tax forms. One exposure brings breach-notification costs, regulator attention, and a hard conversation with leadership, and relying on every staff member to handle each file correctly is a fragile defense. With Kiteworks, policies block or encrypt PII and PHI in HR cases automatically. Retention controls keep files only as long as policy allows, and GDPR and HIPAA reporting is ready when regulators ask, so protection no longer depends on individual judgment.
HR Service Delivery Users
HR Business Partner, HR Service Center Agent, Onboarding Coordinator, all employees
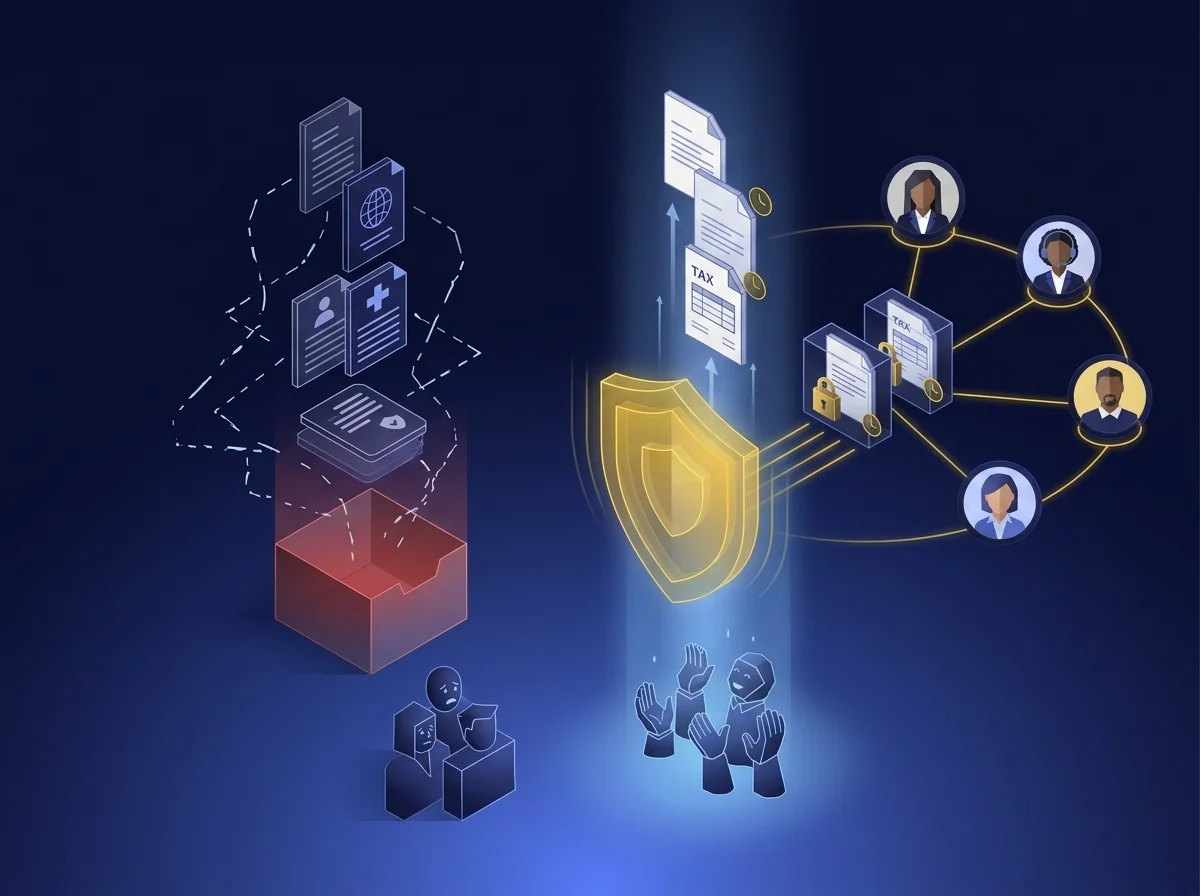
A new hire emails a passport copy and a medical form to HR because the case offers no better option. Employees expect their most personal documents to be handled carefully, and a mishandled file costs trust, while HR staff carry the worry every day. With Kiteworks, employees upload ID and medical documents securely instead of by email. HR sends offer letters and tax forms encrypted, with expiry. Staff stop sending sensitive documents through a channel they cannot control, and employees see their documents treated with care.
Customer Service Management and CRM Administration
CSM Platform Owner, CRM Administrator, Customer Operations Systems Manager
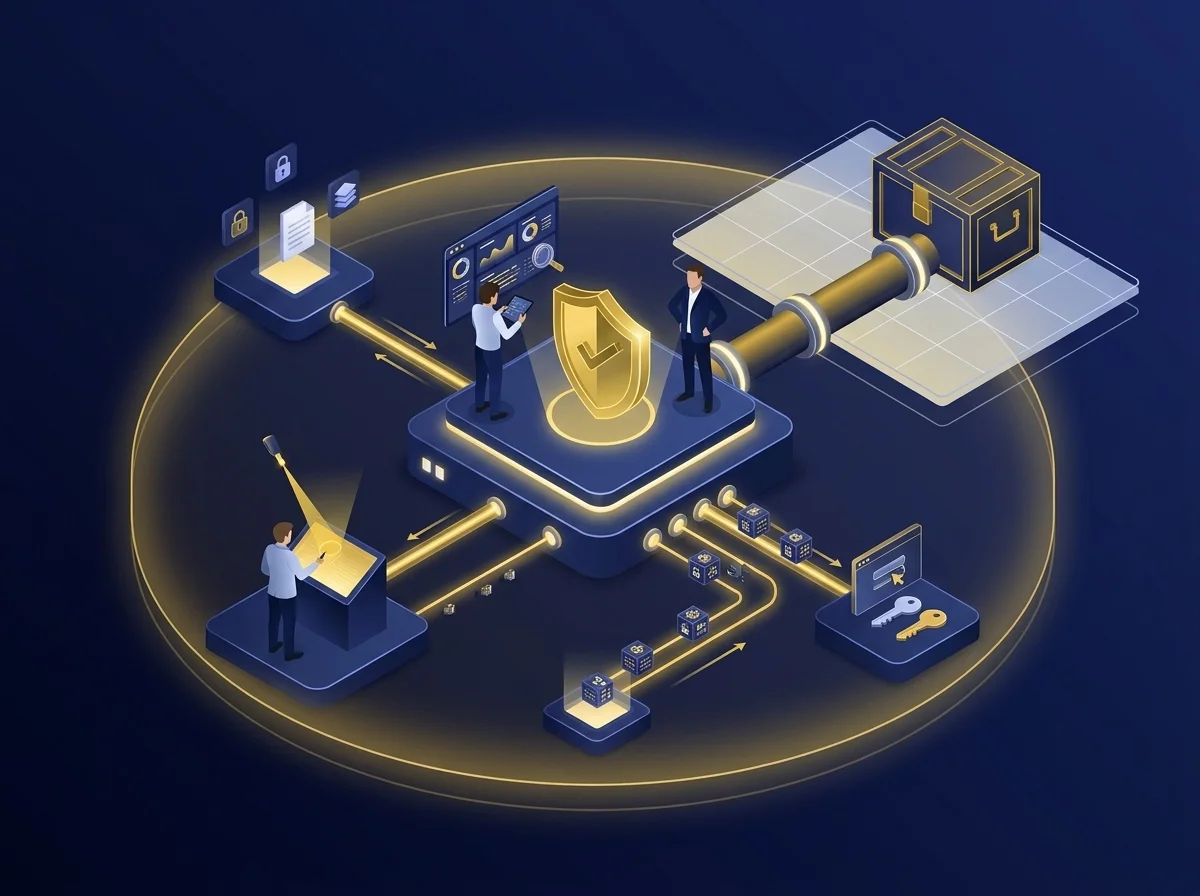
Regulated customers will not send HIPAA, GDPR, PCI DSS, or ITAR data through a channel that cannot prove compliance, and a customer who cannot send safely may take the account elsewhere. The platform owner is the person expected to answer for it. With Kiteworks, regulated customer data gets a compliant transport and audit path, and storage can sit outside the SaaS cloud. The CRM administrator can show a compliance reviewer where files live and who handled them, which protects the revenue tied to regulated accounts.
Customer Service Management and CRM Users
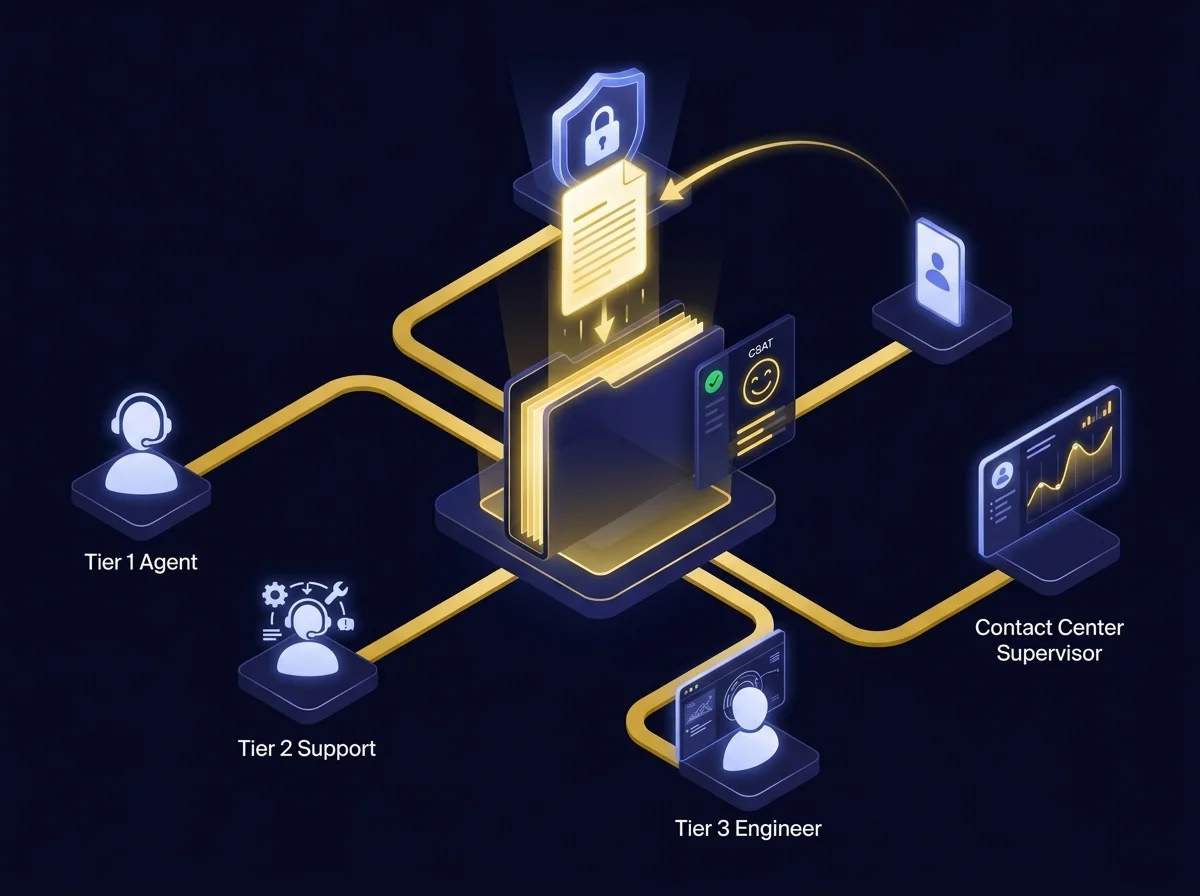
Customer Service Agent, Support Tier 1, Tier 2, and Tier 3 Engineer, Contact Center Supervisor
A support engineer cannot close a case without the customer’s files, and the customer cannot get a large log through email. The case waits, the customer grows frustrated, and the supervisor watches the queue age and the satisfaction score slip. With Kiteworks, support staff request files inside the case, and customers upload from a browser, including very large files. The biggest source of case delay and customer frustration goes away, and the engineer gets the evidence needed to resolve the case while the customer is still engaged.
Low-Code App Development Administration
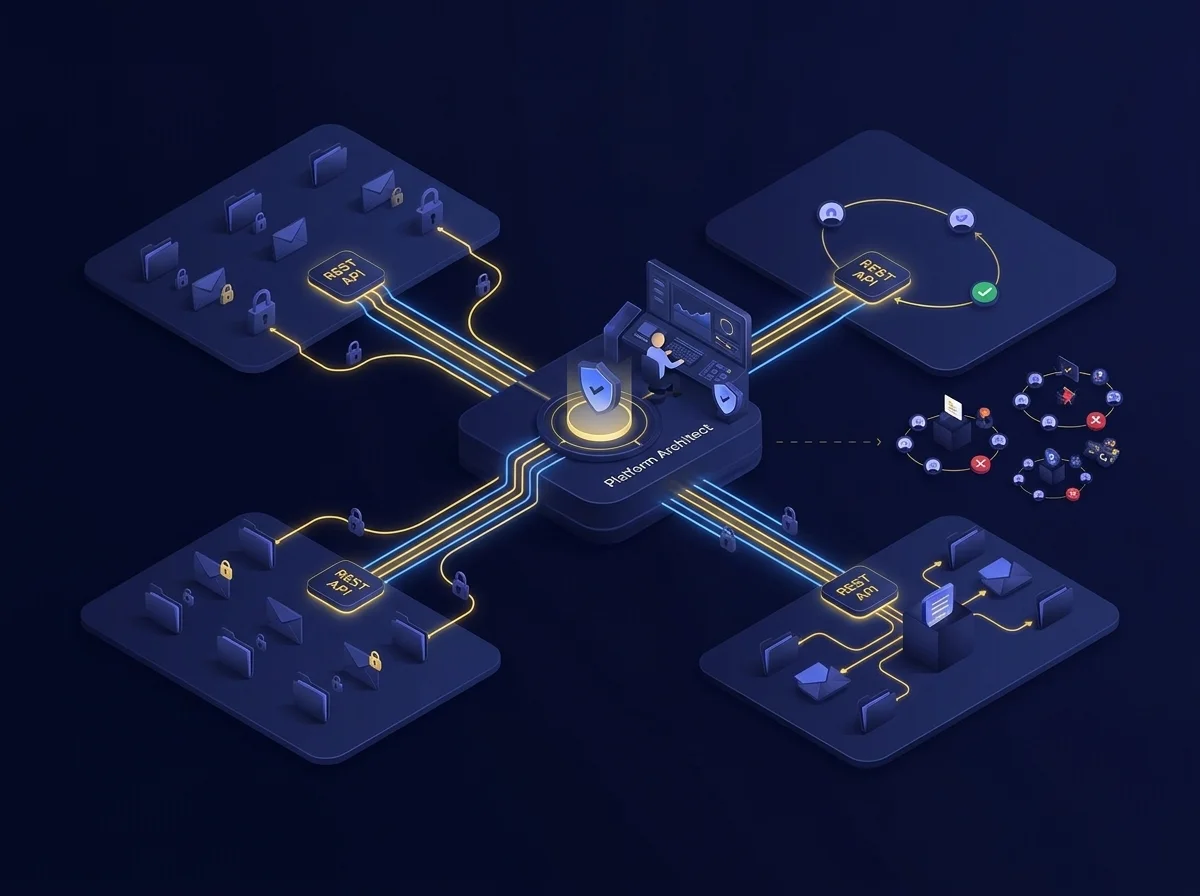
ServiceNow Developer, Platform Architect, Center of Excellence Lead
Every team building an app on the platform ends up writing its own file and email handling, then passing its own security review. The same work repeats across the center of excellence, and each version is one more thing to secure and maintain. With Kiteworks, developers build on REST APIs that automatically protect data and enforce policies, so they don’t have to write and secure file and email handling themselves. The platform architect sets up the control once and reuses it, which saves developer time and review cycles on every future app.
Low-Code App Development Users
Citizen Developer, Business Process Owner
A business process owner with no security or compliance expertise builds an approval app with a document upload form. Without a safe default, this well-meant app can expose sensitive data, unnoticed until an audit. With Kiteworks, apps inherit governed file and email handling automatically, so owners ship faster with safe handling ready before the first file arrives.
Strategic Portfolio Management Administration
SPM Administrator, PMO Tool Owner
A PMO tool owner manages the statements of work and vendor documents that the portfolio shares with outside parties. The footprint is smaller than in other workflows, but the documents are still commercially sensitive, and the owner has no separate way to show who received them. With Kiteworks, statements of work and vendor documents shared externally get the same policy and audit coverage as the rest of the platform. The owner gains that coverage as part of platform-wide control, with no separate project to run for portfolio management.
Strategic Portfolio Management Users
Project, Program, and Portfolio Manager, Resource Manager
A program manager shares a project plan and rate card with an outside vendor, and once the file leaves, nothing controls who forwards it or how long it circulates. Project managers share commercially sensitive documents with vendors all the time, so the exposure repeats every week, across every project. With Kiteworks, they share project documents with outside vendors using view-only, watermarked access. The vendor sees what it needs, the document stays protected, and delivery is not slowed by extra approval steps, a separate tool, or a second login.
Frequently Asked Questions
Files live in a governed Kiteworks folder, not in ServiceNow AI Platform attachment storage, encrypted in transit and at rest. Deployment options include on-premises, self-hosted, Kiteworks-hosted, FedRAMP, or IRAP, with single-tenant architecture, customer-owned keys, and geofencing.
The Data Policy Engine evaluates the sensitivity of the data and the current attributes of the user, then blocks the transfer, limits access to view only, requires approval, or tags the file. The scan verdict is checked before any download occurs.
Kiteworks improves governance across IT Service Management, IT Operations and AIOps, IT Asset Management, Security and Risk, HR Service Delivery, Customer Service Management, Low-Code App Development, and Strategic Portfolio Management.
Policies automatically block or encrypt PII and PHI in HR cases. Retention controls limit file storage duration according to policy, and built-in reporting supports GDPR and HIPAA requirements when regulators request evidence.
Featured Resources
Kiteworks for the ServiceNow AI Platform: Governed Files
Kiteworks for the ServiceNow AI Platform: Governed Files
Kiteworks Integrates with Cyera to Enforce Data Classifications